Multi-Region Networking
Connect workloads across geographic regions while improving redundancy and centralized routing.
Solution:AWS Transit Gateway and regional TGW peering.
Project 03
AWS + Google Cloud + Terraform
Designed and deployed a secure multi-region network connecting AWS infrastructure in Tokyo and São Paulo with Google Cloud environments in Iowa and New York. Business Outcome: Enabled secure, highly available connectivity between AWS and Google Cloud while simplifying network management with Infrastructure as Code.
This project created an enterprise-style multi-cloud network using Terraform Infrastructure as Code. AWS Transit Gateway provides centralized routing between the Tokyo and São Paulo AWS environments, while Google Cloud Network Connectivity Center connects the Iowa and New York GCP networks.
Redundant IPSec VPN tunnels, Cloud Router, and BGP provide encrypted dynamic route exchange between AWS and Google Cloud.
Connect workloads across geographic regions while improving redundancy and centralized routing.
Solution:AWS Transit Gateway and regional TGW peering.
Allow AWS and Google Cloud workloads to communicate securely.
Solution:NCC, Cloud Router, HA VPN, and BGP.
Replace manual provisioning with repeatable and version-controlled deployments.
Solution:Reusable Terraform modules and provider aliases.
Maintain connectivity during tunnel or component failures.
Solution:Multiple regions and four redundant IPSec tunnels.
Protect traffic traveling between cloud providers.
Solution:Encrypted Site-to-Site VPN connectivity.
Automatically exchange routes as the network changes.
Solution:Cloud Router and Border Gateway Protocol.
Add future networks without creating many point-to-point connections.
Solution:TGW and NCC hub-and-spoke networking.
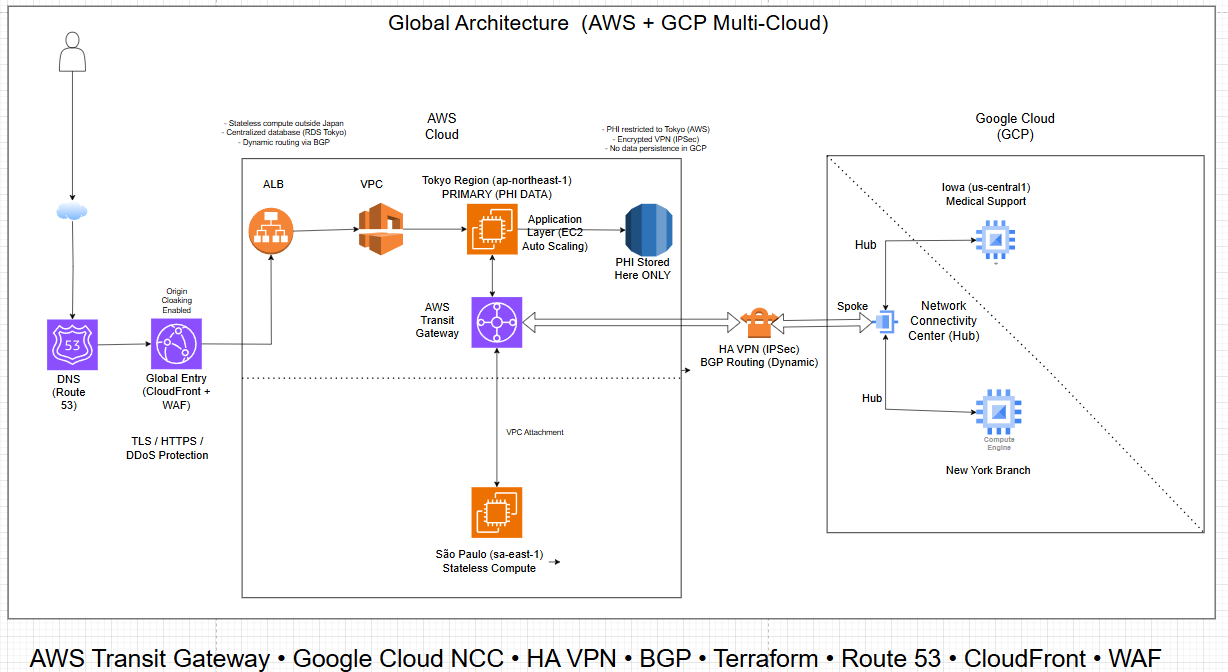
AWS Transit Gateway connects the Tokyo and São Paulo environments. Google Cloud Network Connectivity Center manages the Iowa and New York spokes. HA VPN and BGP provide secure dynamic connectivity between clouds.
Built VPC environments in Tokyo and São Paulo with EC2, load balancing, RDS PostgreSQL, regional Transit Gateways, and Transit Gateway peering.
Extended the AWS environment into Google Cloud using NCC, a transit VPC, Cloud Router, HA VPN, BGP, and test VMs in Iowa and New York.
VPC · EC2 · Application Load Balancer · RDS PostgreSQL · Transit Gateway · TGW Peering · Site-to-Site VPN · CloudFront · AWS WAF
VPC · Compute Engine · Network Connectivity Center · Cloud Router · HA VPN · BGP
Terraform · Terraform Modules · Git · GitHub · VS Code · Draw.io · Markdown
Primary application, database, and networking environment.
Secondary regional compute environment connected through TGW peering.
NCC-connected testing environment.
Remote branch network connected through the NCC architecture.
Multi-region provider configurations initially placed resources in unintended regions.
Resolution:Explicit provider aliases were assigned to the appropriate Terraform modules.
Resources in separate modules required identifiers that were not exposed correctly.
Resolution:Variables and outputs were added to establish clear module interfaces.
Incorrect route propagation and advertised CIDR ranges prevented communication.
Resolution:VPN status, BGP sessions, TGW routes, and GCP routes were validated and corrected.
Review the complete Terraform source code, module structure, diagrams, screenshots, deployment evidence, and full technical report.